Web application testing
Find the flaws attackers use in your web apps.
Authenticated and unauthenticated testing of your web apps against OWASP Top 10 and business-logic flaws.
 Draft my scope with Kai
- Typical length
- 5–10 days
- Standard
- OWASP Top 10
- You get
- Findings per role and flow
- Testers
- CREST certified
What we test
- Authentication and session handling
- Access control and tenant separation
- Injection, XSS and request forgery
- Business-logic abuse
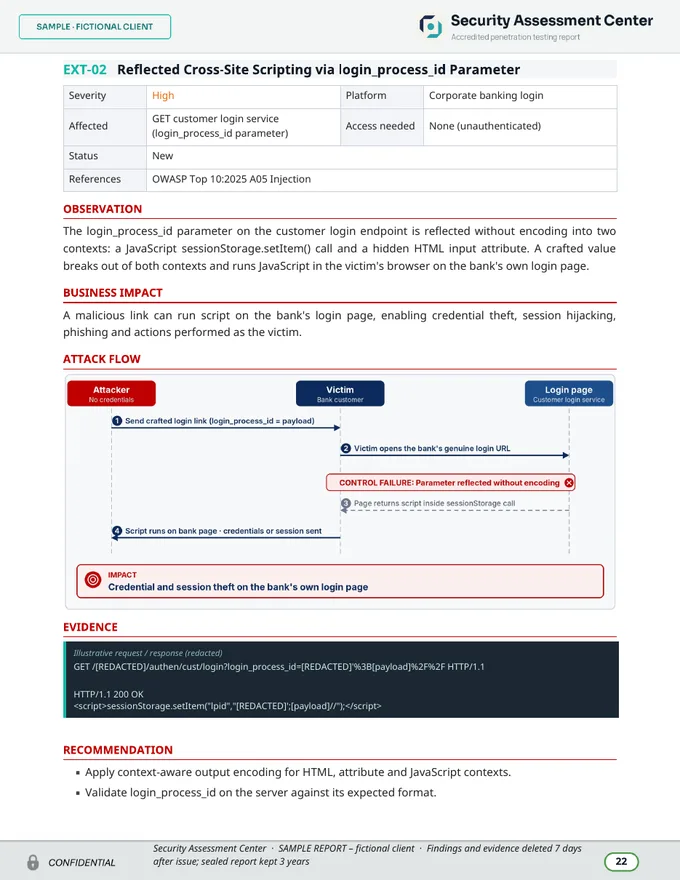
See what you'll receive
A watermarked page from a real sample report.
View sample reportHow it works
- 1Align
We agree scope, accounts and rules of engagement.
- 2Discover
We map every target, role and entry point.
- 3Analyse
Live findings appear in your workspace as we confirm them.
- 4Penetrate
We prove impact safely, with evidence.
- 5Transform
Fix guidance, retest and a sealed report.
See your estimate in 2 minutes.
Tell us what needs testing. An advisor replies within one business day with next steps and portal onboarding.